Stop unauthorized access before it ships
depthfirst catches broken authorization, privilege escalation, IDOR, and subscription tier bypasses by reasoning about what your code is supposed to do
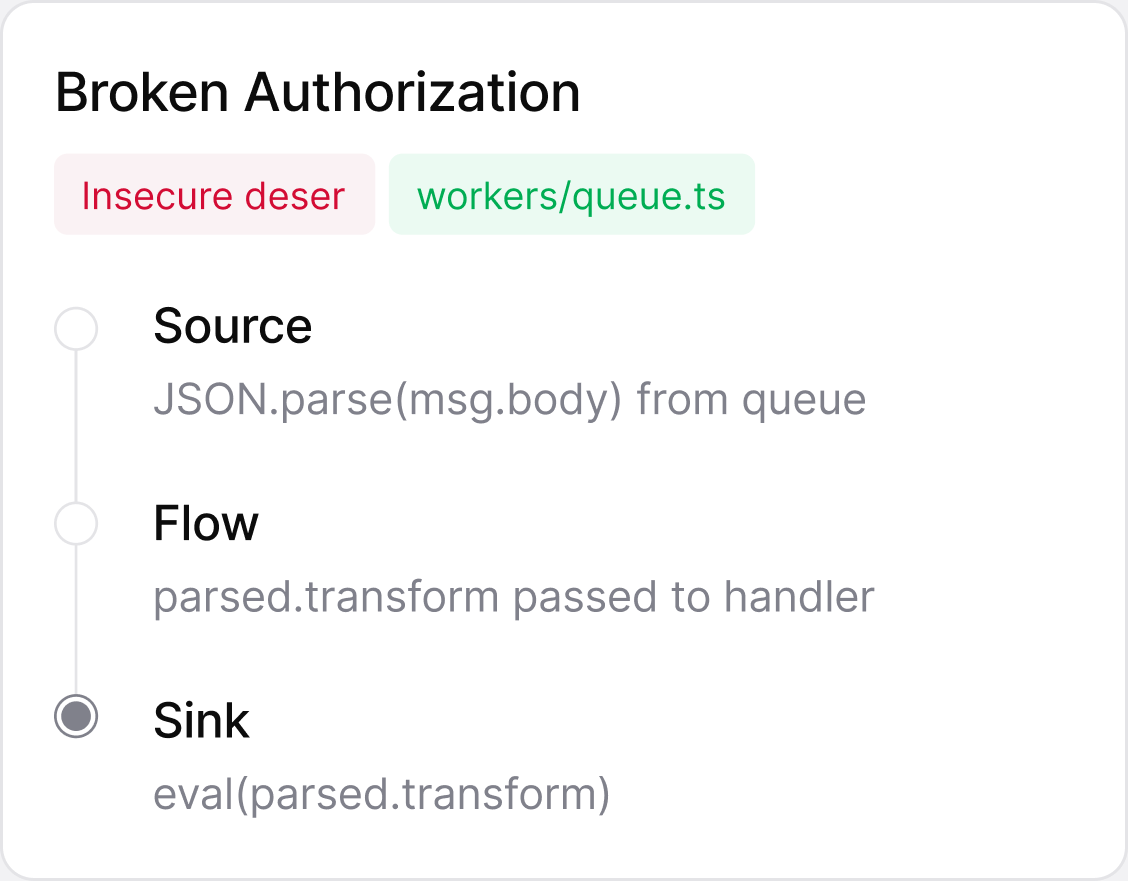
We understand your code like a Security Engineer, tracing business logic, mapping cross-service data flows, and surfacing real vulnerabilities, fixing them autonomously.

depthfirst catches broken authorization, privilege escalation, IDOR, and subscription tier bypasses by reasoning about what your code is supposed to do
depthfirst maps data flows across service boundaries, exposing attack paths that only exist between components—where an input in one service reaches a vulnerable sink in another.

depthfirst connects individual low-severity findings into exploitable paths by mapping how weak points chain together through your application’s data flows and control logic.

Surface broken authorization, privilege escalation, and logic flaws by analyzing data flow, service interactions, and runtime behavior across your codebase.
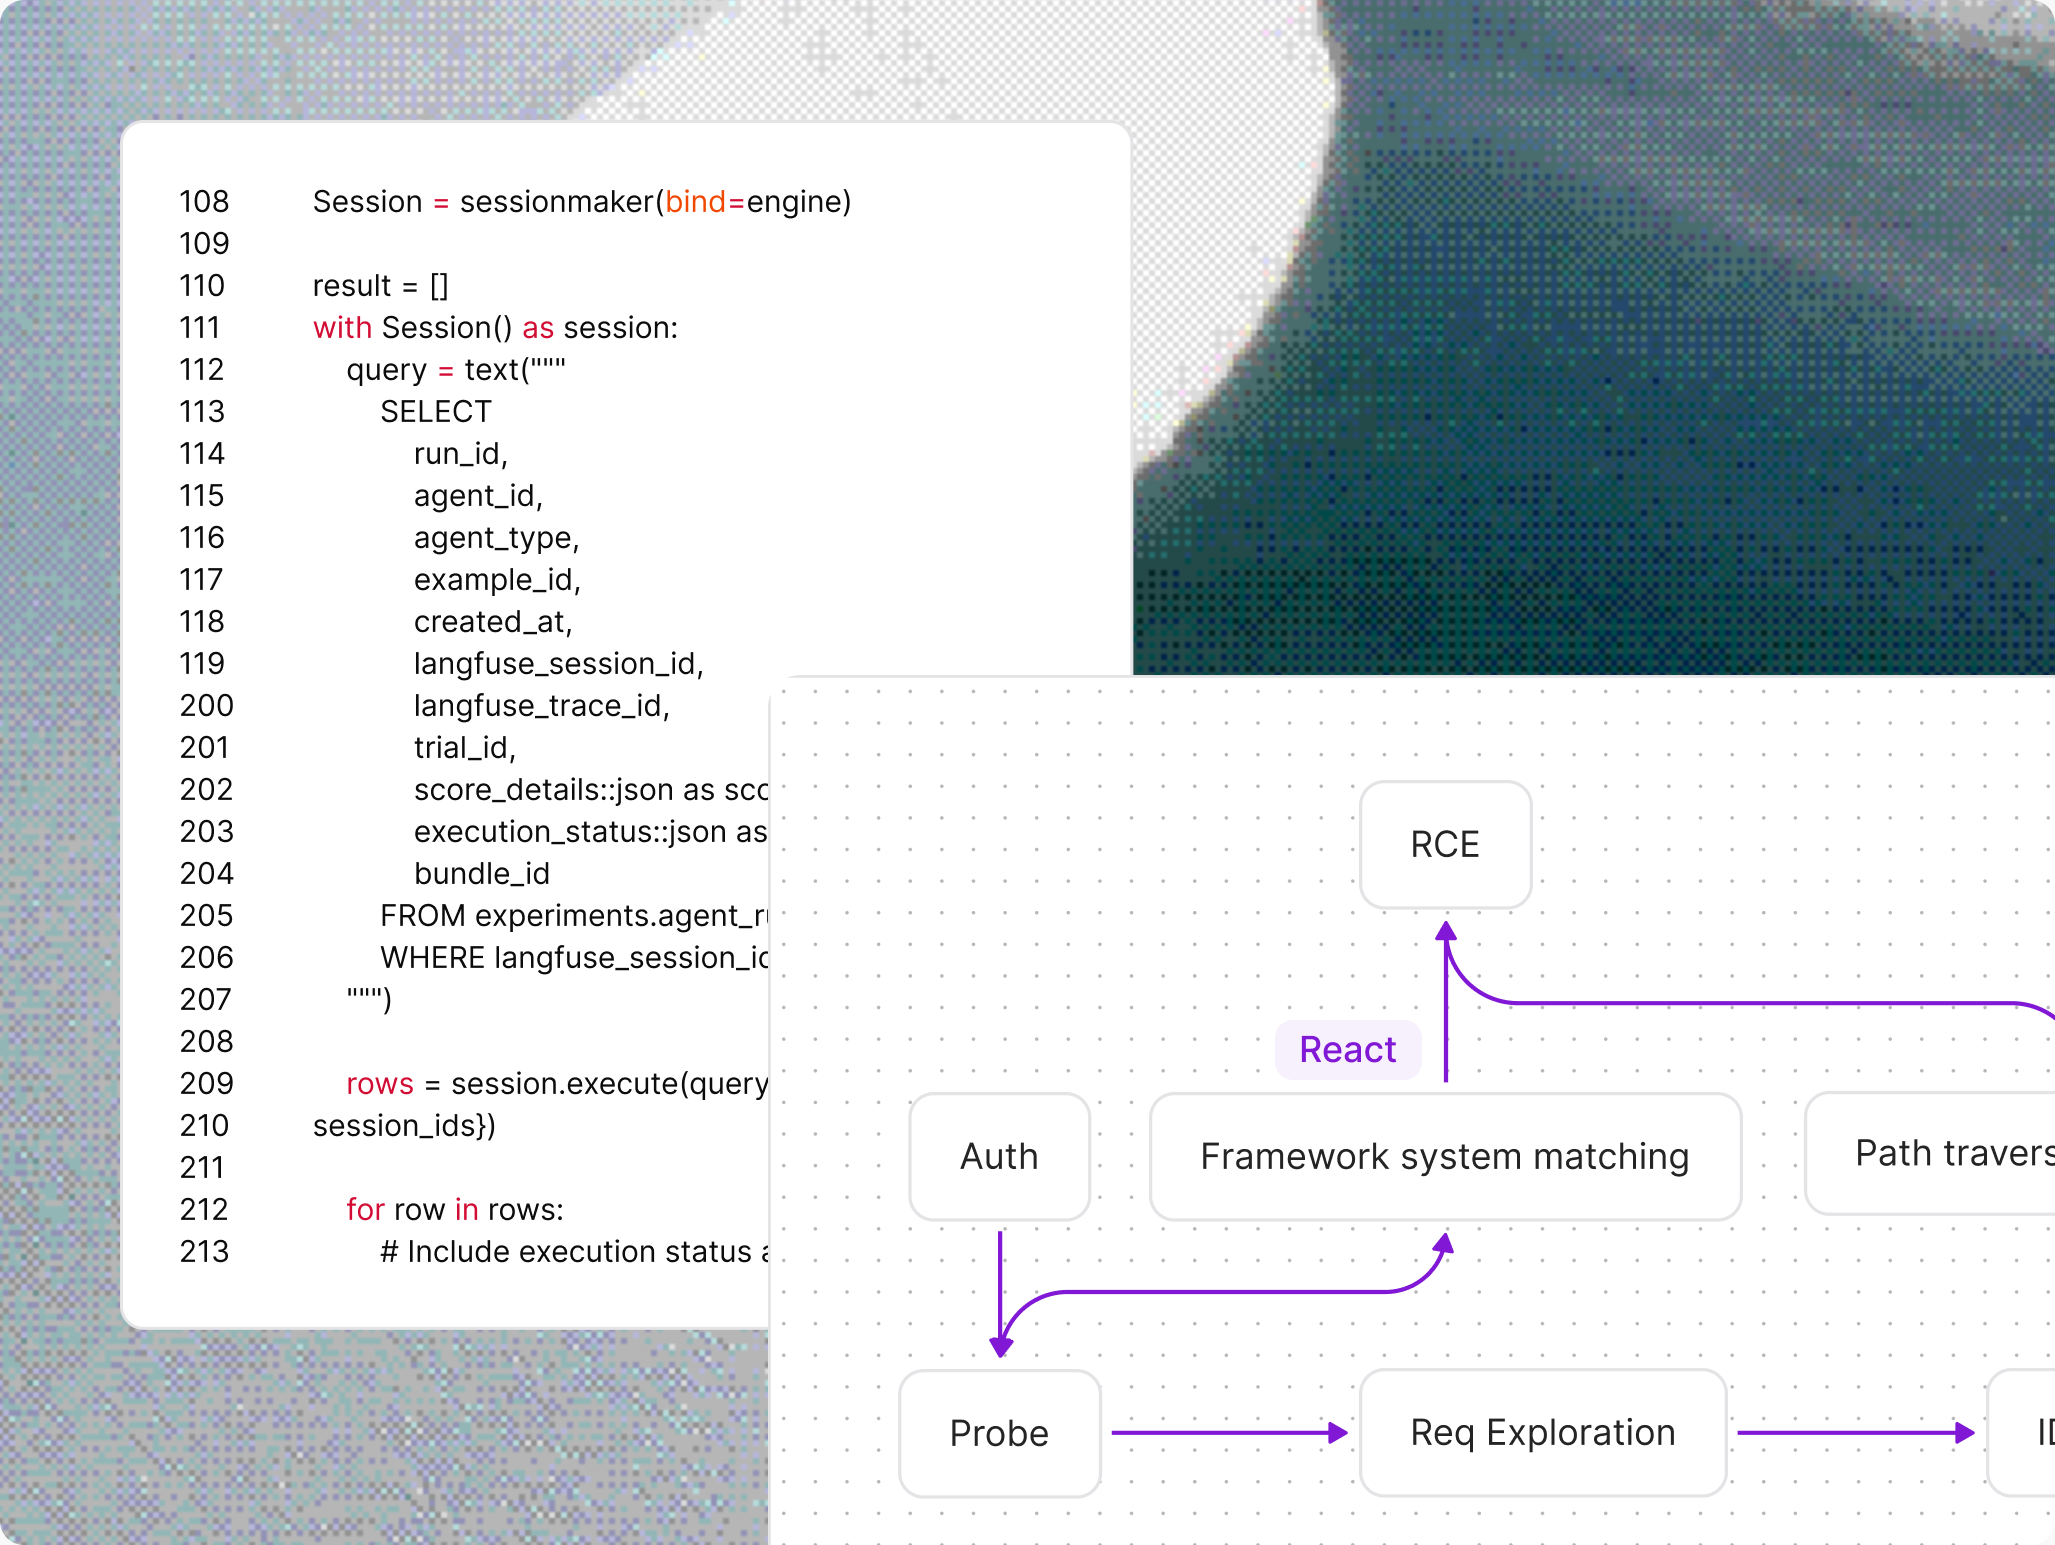
Eliminate false positives with full evidence trails and exploitation conditions. When conditions are met, depthfirst runs a dynamic test against your application to confirm the exploit.
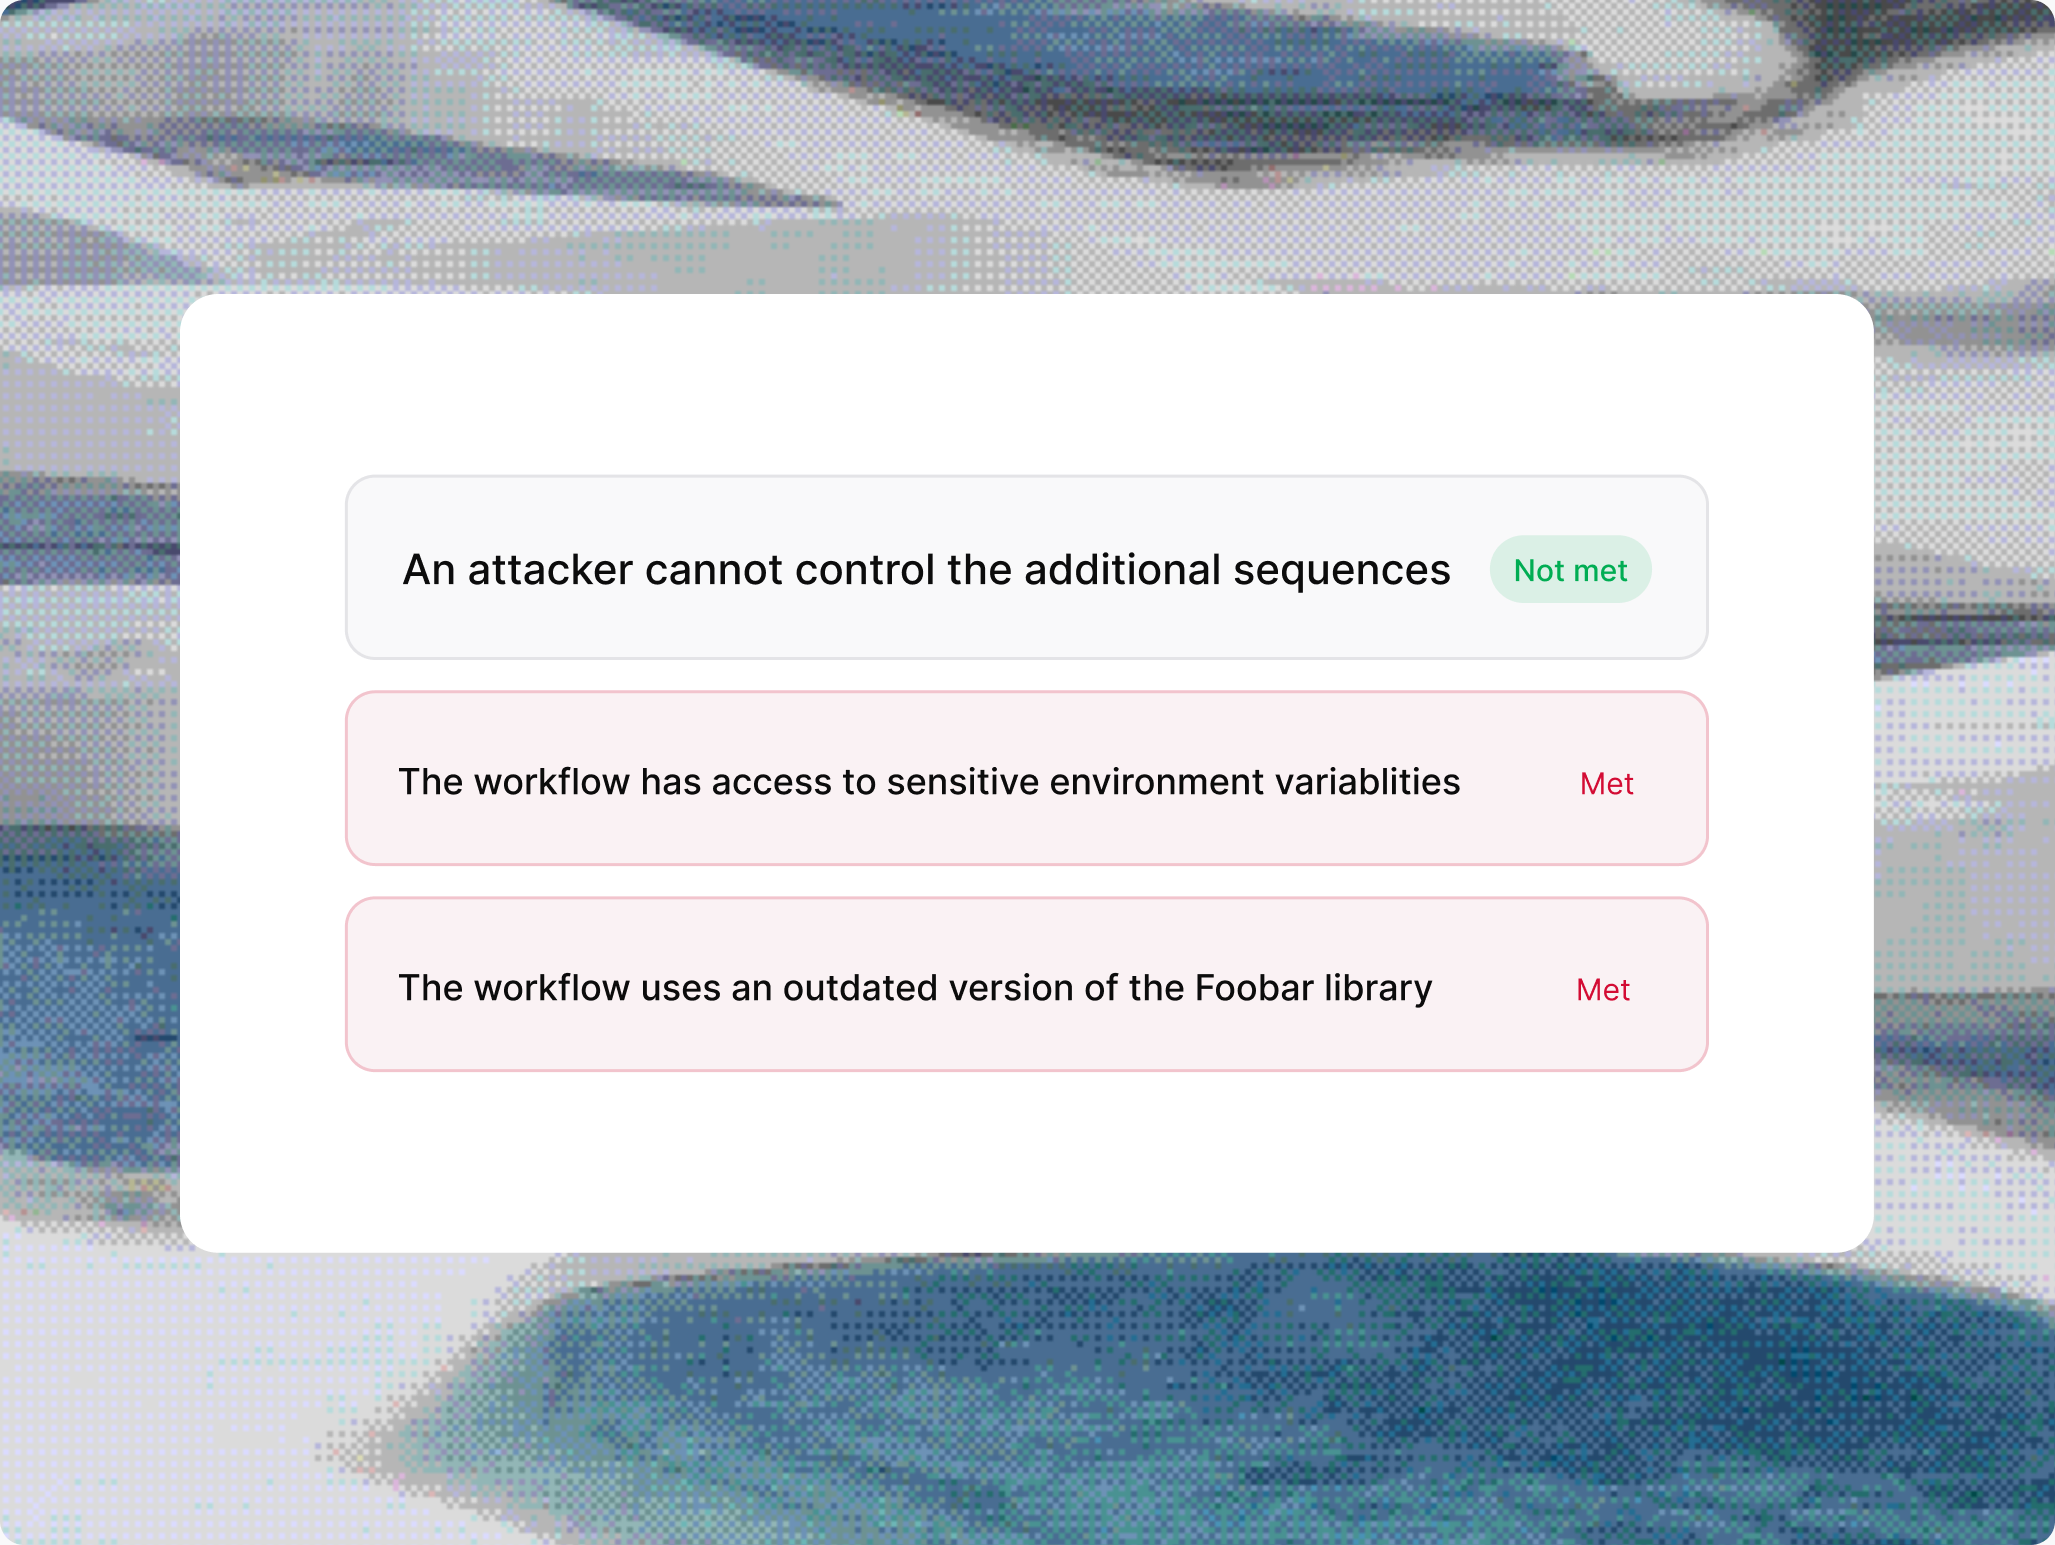
Ship fixes faster with pull request comments that match your conventions. Developers review and merge without context-switching or manual remediation.
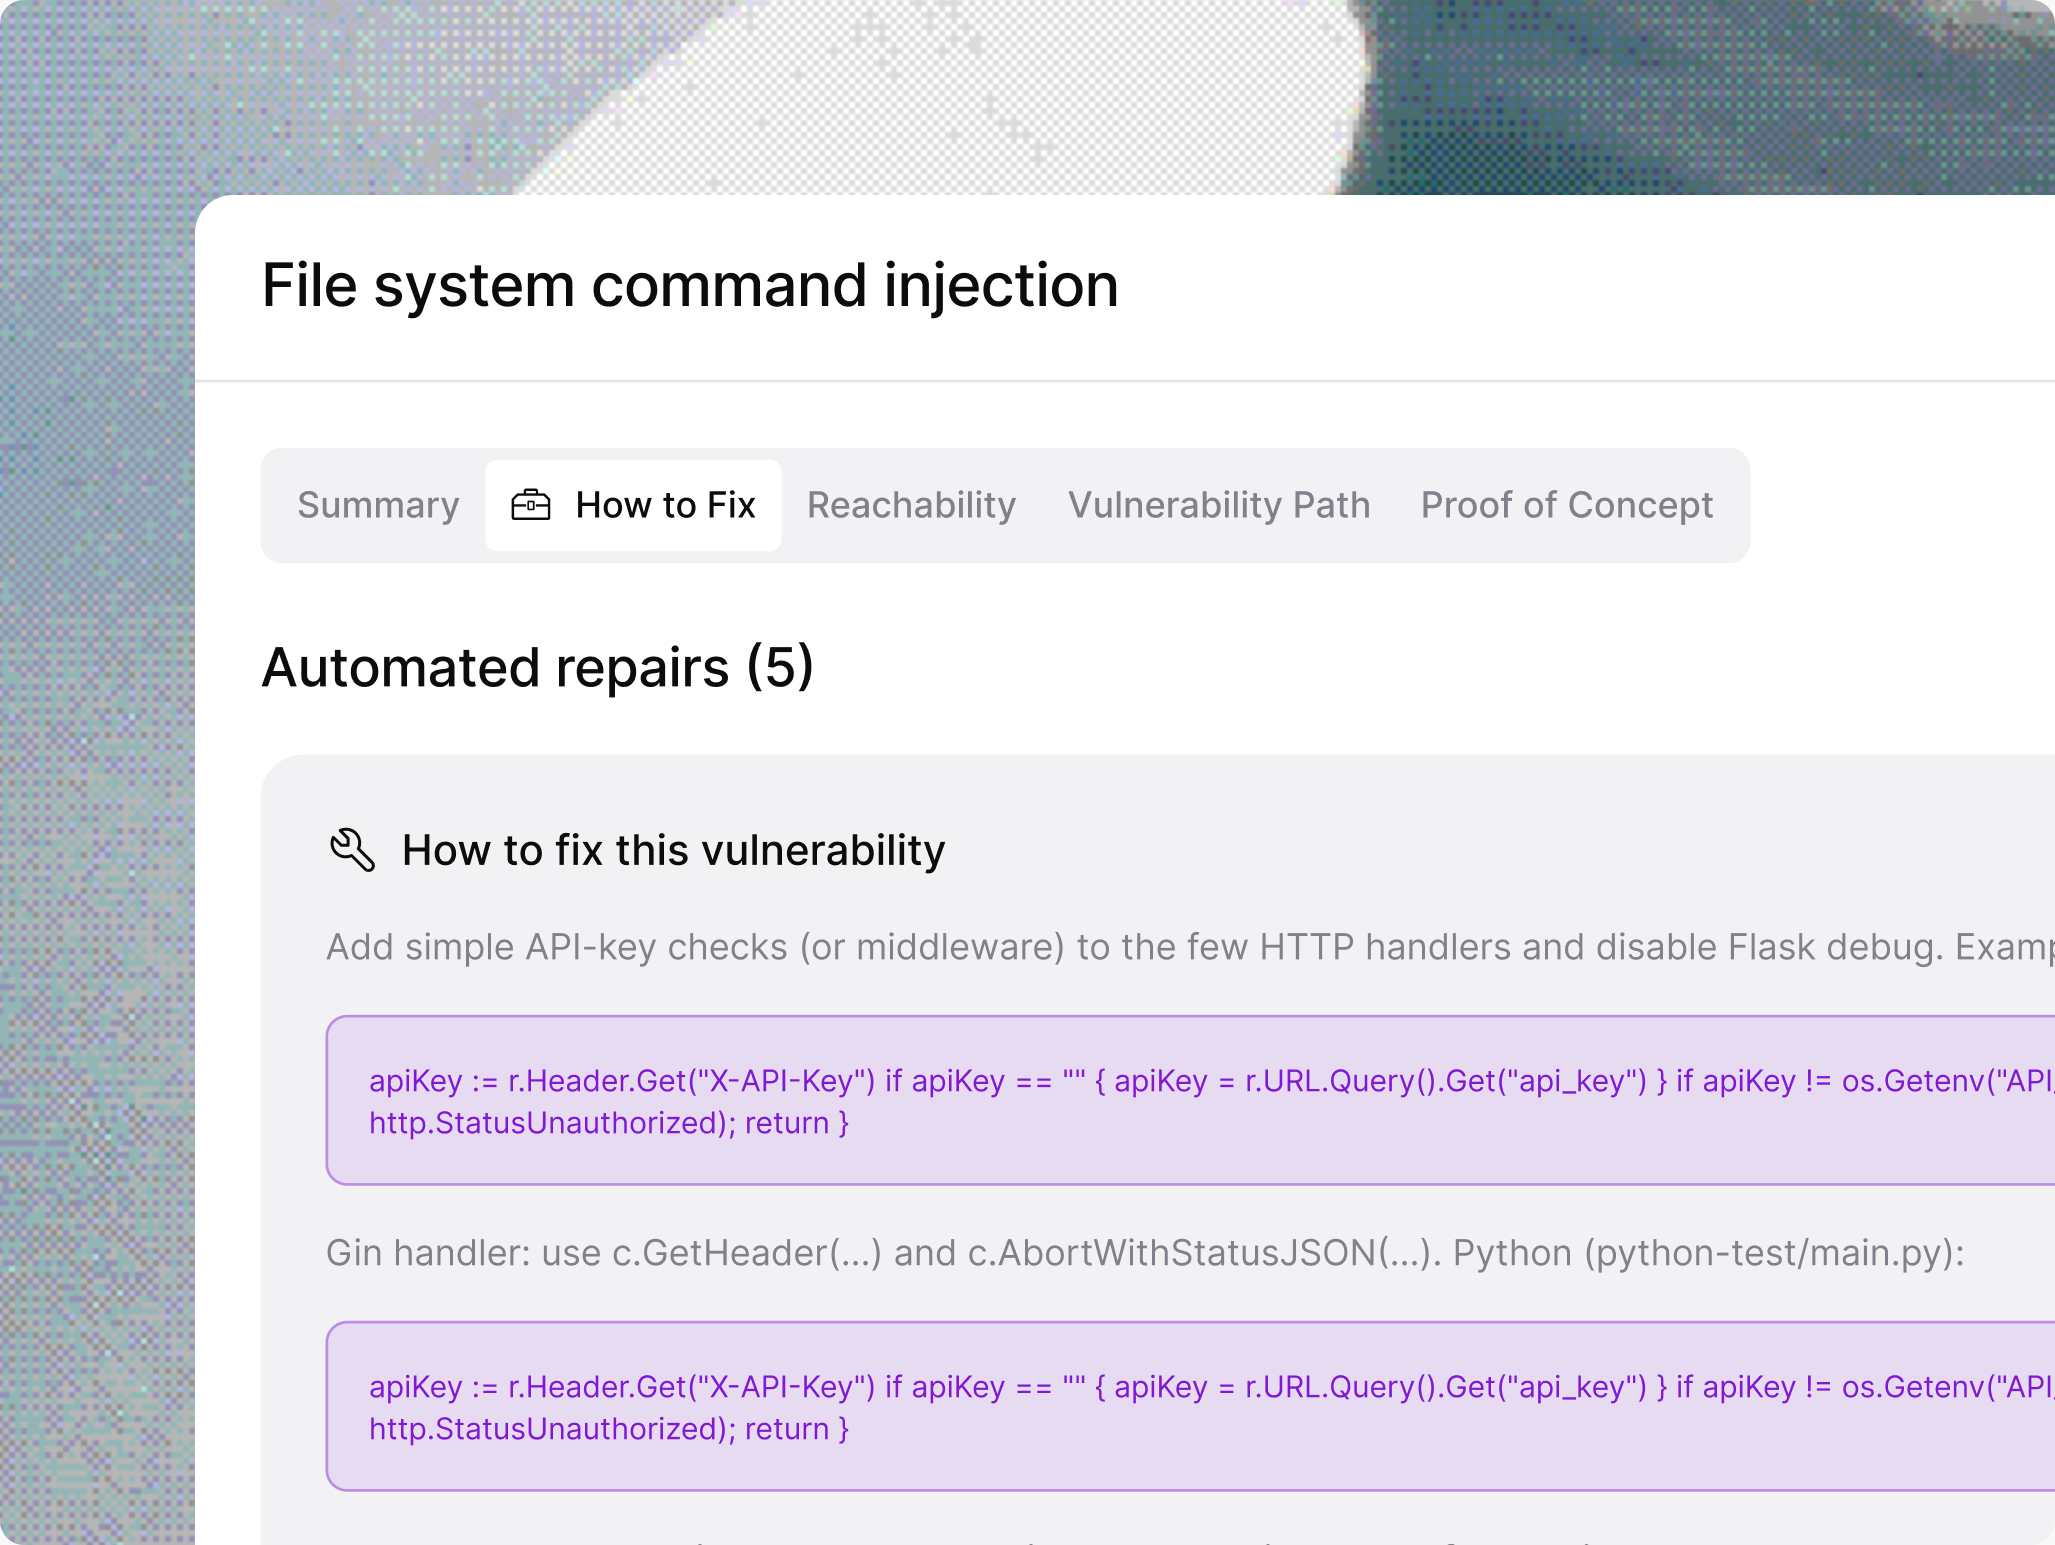
Analyze your entire codebase to surface the full landscape of vulnerabilities.
Run on every pull request in 2–5 minutes, catching new vulnerabilities before merge.
Findings surface as PR comments with one-click access to full context and generated fixes.
Developers give feedback directly in GitHub to train the system and improve scanning accuracy.
Detect malicious behavior before it spreads through your environment.
Confirm which vulnerabilities are exploitable by testing your running application with real attack paths.
depthfirst attacks your running applications continuously, proving at runtime which vulnerabilities are actually exploitable and re-testing every fix after merge.
Trace risk through your full dependency tree and surface only the vulnerabilities with a real execution path to them.
depthfirst traces every dependency to the code that actually calls it, so you fix the handful of vulnerabilities with a real path into your application instead of the whole SBOM.
Detect and validate credentials across your codebase, CI/CD pipelines, and runtime environments.


