Software supply chain security
Software supply chain security for agentic development
Secure your entire software supply chain. Cycode protects workstations and CI/CD pipelines from malicious and vulnerable dependencies, detects secrets everywhere, and governs AI tools and interactions.


Analyst recognition
- Leader2026 Gartner® Magic Quadrant™ for Software Supply Chain Security, the first Magic Quadrant for the category
- #1Software Supply Chain Security use case, 2025 Gartner® Critical Capabilities for AST
- LeaderOverall Leader in the Leadership Compass for Software Supply Chain Security 2026
- LeaderLeader in the GigaOm Radar for Software Supply Chain Security
See how our customers use Cycode to build and deliver secure applications
Why now
Your supply chain now includes
the AI that writes your code
Every package an assistant adds, every action a pipeline runs, and every secret a build touches is part of what you ship. Point tools see one stage at a time.
AI pulls in dependencies
Coding assistants and agents add packages faster than anyone reviews them. Each one becomes part of your supply chain.
Attackers target the pipeline
Shai-Hulud, tj-actions, and LiteLLM moved through registries, CI workflows, and build steps, not just packages.
Stages are connected
Risk that starts in a dependency and ends in a leaked pipeline secret looks like two unrelated findings in two tools. Cycode connects them.
Coverage
One platform for every
stage of the chain
Our own scanners cover the full path from a developer machine to a signed artifact, and each stage links to the next in one view.
Developer workstation
Block malicious packages on developer machines in real time, whether a developer or a coding agent runs the install.
Workstation ProtectionOpen source
Find vulnerable and risky packages with reachability and exploitability analysis.
SCASecrets and NHIs
Detect hardcoded secrets across repositories and productivity tools. Correlate them to non-human identities. Prevent exposure in AI prompts and actions.
Secrets detectionSource control and CI/CD
Find pipeline misconfigurations and prevent unauthorized access and malicious injection.
CI/CD securityBuild and runtime
Monitor live pipeline execution for supply chain attacks in progress and harden builds to protect artifact integrity.
CI/CD runtimeCode leakage
Monitor public platforms and dark web forums for exposed source code.
Code leakage detectionSBOM and AIBOM
Generate software and AI bills of materials for dependency and AI tool transparency.
SBOM and AIBOMOne Context Intelligence Graph
Every stage feeds one graph, so a finding at one stop shows what it reaches at the next.
See the graph
Context Intelligence Graph
See how supply chain
risk actually travels
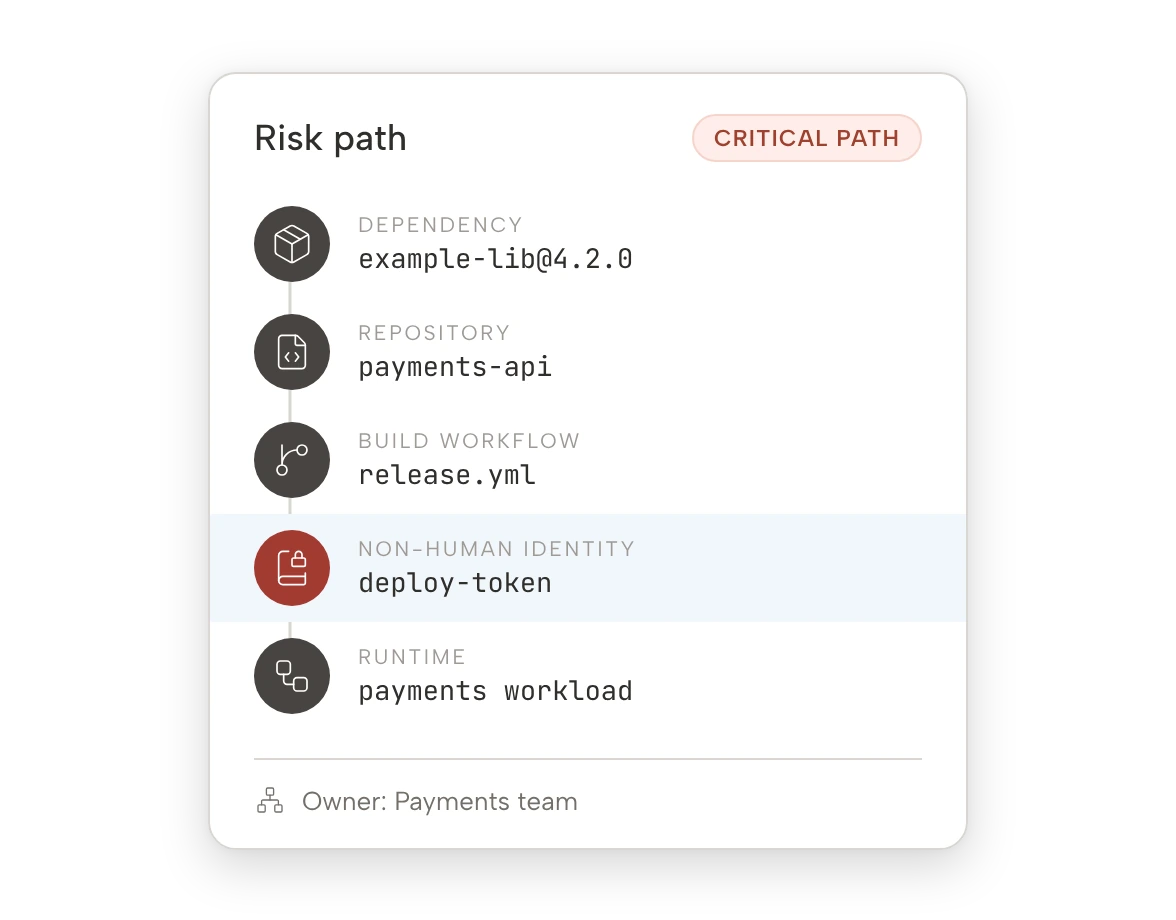
The Context Intelligence Graph connects ownership, repositories, pipelines, and runtime. It adds exploitability analysis and dynamic risk scoring, so teams fix the issues that matter first.
From package to pipeline
Trace a risky dependency to the repositories, pipelines, and builds it reaches.
From secret to identity
See which non-human identity a leaked secret unlocks and what it can touch.
From finding to owner
Route every issue to the team and service that owns it.

Build securely with one
connected platform.
AI supply chain
Your AI tools are part
of the supply chain
AI Visibility discovers the coding assistants, MCP servers, and shadow AI in use across development. AI Governance enforces policy with an AIBOM.
AI Visibility
Discover coding assistants, MCP servers, and shadow AI, with deep Cursor and Anthropic Console integrations.
AI Governance
Enforce policy on which AI tools and MCP servers agents can use, backed by an AIBOM.
Workstation Protection
Block malicious packages and enforce cooldown policies on every developer workstation.


Compliance
Report against the
frameworks your auditors ask for
Generate SBOMs and AIBOMs and collect the evidence teams need to report against NIST SSDF 1.1 and 1.2, SOC 2, ISO 27001, and CIS Benchmarks.
“SBOMs are like the ingredients label on your food. Our customers expect that level of transparency. Cycode helps us deliver it. It automatically pulls and assembles the information we need to generate SBOMs at scale, significantly easing the operational burden on our team.”


FAQ
Frequently asked questions about software supply chain security
What is software supply chain security?
Software supply chain security protects everything that goes into the software you ship: open source packages, source control, CI/CD pipelines, build systems, secrets, and the AI tools that now write and change code. The goal is to keep malicious or vulnerable components, exposed secrets, and compromised pipelines from reaching production.
What is the best solution for software supply chain security?
The best solution covers every stage of the chain in one platform, because point tools each see one stage at a time. Cycode covers developer workstations, open source, secrets and non-human identities, source control and CI/CD, build and runtime, code leakage, and SBOM and AIBOM, and connects the findings in one Context Intelligence Graph. Cycode is a Leader in the 2026 Gartner® Magic Quadrant™ for Software Supply Chain Security.
How is software supply chain security different from SCA?
Software composition analysis (SCA) finds vulnerable and risky open source packages. Software supply chain security is broader: it also covers the developer workstation, secrets and non-human identities, source control, CI/CD pipelines, builds, code leakage, and the AI tools used in development. SCA is one stage of the chain.
How does Cycode protect CI/CD pipelines?
Cycode finds pipeline misconfigurations and prevents unauthorized access and malicious injection in source control and CI/CD. It also monitors live pipeline execution for supply chain attacks in progress and hardens builds to protect artifact integrity.
How do AI coding assistants affect software supply chain risk?
Coding assistants and agents add packages faster than anyone reviews them, and each one becomes part of your supply chain. The assistants, MCP servers, and models are part of the chain too. Cycode blocks malicious packages on developer workstations whether a developer or a coding agent runs the install, discovers the AI tools in use across development, and enforces policy with an AIBOM.
What should a software supply chain security platform include?
A software supply chain security platform should cover the full path from a developer machine to a signed artifact: workstation protection, open source analysis with reachability and exploitability, secrets and non-human identity detection, source control and CI/CD security, build and runtime monitoring, code leakage detection, and SBOM and AIBOM generation. Each stage should link to the next in one view, so a finding at one stage shows what it reaches at the next.
Does Cycode generate SBOMs and support compliance requirements?
Yes. Cycode generates software and AI bills of materials (SBOMs and AIBOMs) and collects the evidence teams need to report against NIST SSDF 1.1 and 1.2, SOC 2, ISO 27001, and CIS Benchmarks.
See your whole software supply chain in one view
One platform and one graph across workstations, dependencies, secrets, pipelines, builds, and AI tools.
Book a demo